

The System Development Life Cycle (SDLC) is a structured process that guides information systems’ creation, deployment, and maintenance from inception to retirement. For government and defense projects (where precision and security are paramount) the SDLC provides an essential framework that ensures methodical development, rigorous testing, and ongoing maintenance of critical systems.
Unlike commercial software development, government and defense projects face unique challenges including stringent security requirements, complex compliance regulations, and the need for systems that can function flawlessly in high-stakes environments. The SDLC addresses these challenges by breaking down the development process into manageable phases, each with specific objectives, deliverables, and quality gates.
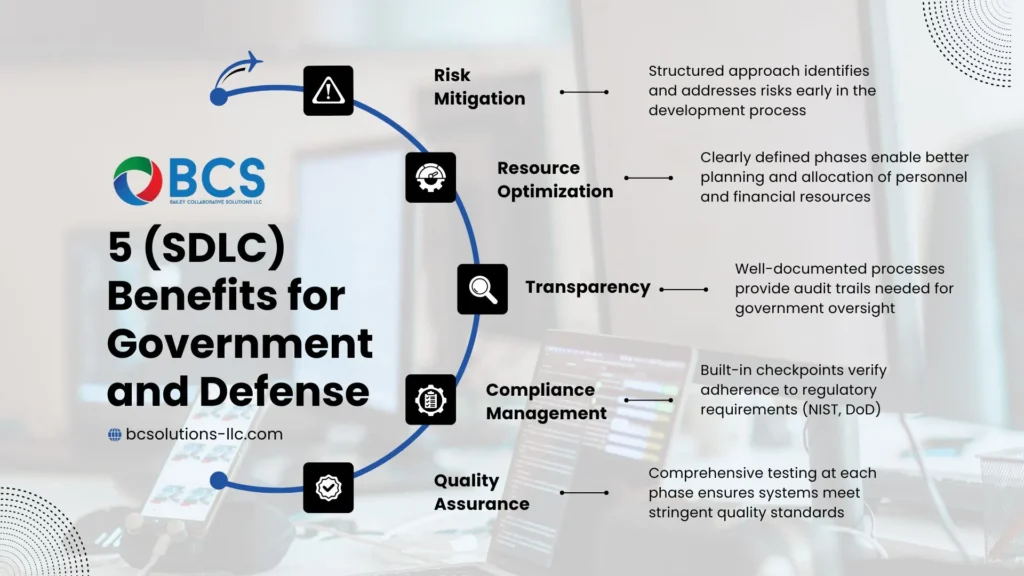
What makes this approach essential for national security applications? How can organizations implement it effectively? And what best practices ensure success? This comprehensive guide explores these questions while examining how the SDLC delivers systems that meet the exacting requirements where system failures could have serious security implications.
I. Understanding SDLC Models in Government & Defense
Before breaking down the individual phases of the System Development Life Cycle (SDLC), it’s important to explore the different models used in government and defense projects. Each model has its own strengths, and the choice depends on factors such as project scope, security needs, and operational demands.
Government and defense agencies carefully select an SDLC model based on the complexity of the project, security classifications, and stakeholder expectations. The chosen approach plays a key role in ensuring project success, integrating security at every stage, and meeting compliance requirements throughout the system’s lifecycle.
| SDLC Model | Key Characteristics | Government/Defense Application | Security Integration Approach |
| Waterfall | Sequential phases with formal gates | Used for weapons systems with well-defined requirements | Security reviews conducted at specific milestones |
| Incremental | Phased delivery of capabilities | Applied in command and control systems | Security assessment performed at each increment |
| Spiral | Risk-driven iterative approach | Common in intelligence analysis platforms | Ongoing threat modeling and risk mitigation |
| Agile-Hybrid | Iterative with built-in compliance checkpoints | Used for tactical communication systems | Security integrated into development sprints with formal documentation |
| DevSecOps | Continuous integration and delivery | Essential for cyber defense platforms | Automated security testing integrated into the development pipeline |
Choosing the right SDLC model requires a balance between operational priorities, security mandates, and regulatory compliance. For classified projects, models that emphasize thorough documentation and verification steps are often required by policy. However, many agencies are adopting more flexible approaches, such as Agile-Hybrid and DevSecOps, while ensuring compliance through automated security validation and continuous authorization mechanisms.
A solid understanding of these SDLC models lays the groundwork for successfully implementing the seven phases of the SDLC in government and defense environments.
II. The 7 Phases of the System Development Life Cycle (Explained Briefly)
The SDLC consists of seven distinct phases, each critical to successful system development. In government and defense contexts, these phases often involve additional security considerations and compliance checks.
1. The Planning Phase
The planning phase establishes the foundation for the entire project. Engineers must define project scope, objectives, and feasibility while considering the unique constraints of government and defense applications. This phase includes identifying stakeholders, establishing preliminary budgets, and conducting initial risk assessments.
For example: a military communication system project would begin by clarifying classification requirements, operational environments (field vs. command center), and integration needs with existing defense information systems.
| Planning Phase Activities | Government/Defense Considerations |
| Project Scope Definition | Must consider classification levels and need-to-know restrictions |
| Feasibility Studies | Analysis must account for strict security and performance requirements |
| Initial Risk Assessment | Includes national security implications and threat modeling |
| Resource Planning | Considers cleared personnel requirements and secure facility needs |
| Stakeholder Identification | Includes military/government hierarchy and decision authorities |
2. The Analysis Phase
During the analysis phase, systems engineers gather and document detailed requirements. For defense projects, this often involves extensive consultation with military personnel, security experts, and compliance officers to ensure all operational and regulatory needs are captured.
Consider a missile defense system: engineers would conduct thorough threat analyses, define detection parameters, and establish real-time performance requirements while ensuring compliance with arms control treaties and military standards.
| Analysis Phase Activities | Government/Defense Considerations |
| Requirements Gathering | Must capture classified and unclassified requirements separately |
| Gap Analysis | Identifies potential security vulnerabilities in current systems |
| User Needs Documentation | Accounts for multiple user roles with varying security clearances |
| Process Mapping | Documents secure workflows and data handling procedures |
| Regulatory Compliance Identification | Maps relevant NIST, DoD, and other regulatory requirements |
3. The Design Phase
The design phase transforms requirements into detailed system architecture and design specifications. In government and defense projects, this involves addressing complex security architecture concerns and ensuring designs meet relevant standards like NIST SP 800-53 or DoD 8500.
For a secure government database system, engineers would create detailed data flow diagrams, encryption schemes, access control matrices, and system boundary definitions while incorporating zero-trust architecture principles.
| Design Phase Activities | Government/Defense Considerations |
| System Architecture Definition | Must implement defense-in-depth security approaches |
| Database Design | Includes data classification schemes and compartmentalization |
| Interface Design | Considers secure HMI (Human-Machine Interfaces) principles and multi-level security |
| Security Controls Specification | Implements appropriate controls from NIST SP 800-53 |
| Technical Specifications | Addresses hardening requirements and secure configuration baselines |
4. The Development Phase
During development, the system design is transformed into working code and hardware components. For government and defense projects, this often involves working in secure environments with restricted development tools and specialized security libraries.
A defense contractor developing cryptographic modules would implement code in accordance with FIPS 140-2 requirements, using approved algorithms, secure coding practices, and code signing procedures throughout the build process.
| Development Phase Activities | Government/Defense Considerations |
| Code Development | Must follow secure coding standards (CERT, CWE Top 25) |
| Configuration Management | Requires robust version control with security tagging |
| Security Implementation | Incorporates approved cryptographic modules and protocols |
| Unit Testing | Includes specific tests for security controls and boundary conditions |
| Code Reviews | Often requires multiple reviewers with appropriate subject matter expertise |
5. The Testing Phase
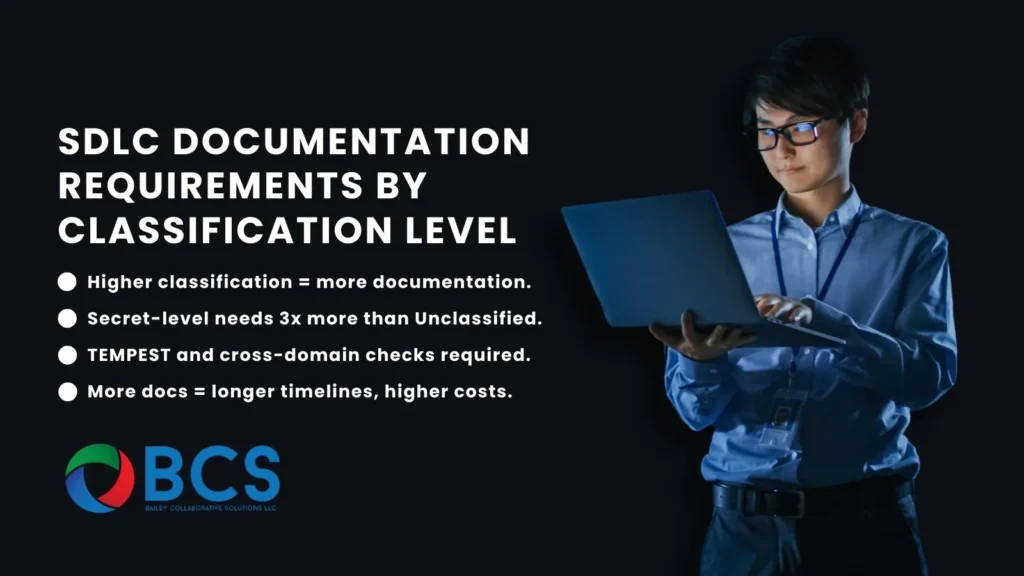
The testing stage for SDLC is particularly rigorous in government and defense contexts. Systems must undergo extensive functional testing, security assessments, and formal certifications before deployment.
For example: a new air traffic control system would undergo thorough performance testing, security vulnerability assessments, and formal certification and accreditation processes, including penetration testing by dedicated red teams.
| Testing Phase Activities | Government/Defense Considerations |
| Functional Testing | Verifies system performance under various operational conditions |
| Security Testing | Includes penetration testing, vulnerability scanning, and code analysis |
| Integration Testing | Ensures secure interfaces with other government systems |
| User Acceptance Testing | Often conducted in simulated operational environments |
| Certification & Accreditation | Formal process required for authorization to operate (ATO) |
6. The Implementation Phase
Implementation involves deploying the tested system into the operational environment. This phase requires careful planning to minimize disruption to critical government and defense operations.
When deploying a new command and control system for a military installation, implementation would include secure data migration, phased rollout procedures, and contingency plans for immediate rollback if issues arise.
| Implementation Phase Activities | Government/Defense Considerations |
| Deployment Planning | Accounts for operational security during cutover |
| Data Migration | Includes secure transfer of classified information |
| User Training | Incorporates operational security procedures |
| System Documentation | Develops classified and unclassified documentation sets |
| Operational Transition | Often requires formal acceptance by government authorities |
7. The Maintenance Phase
The maintenance phase involves ongoing support, updates, and eventual decommissioning of the system. In government and defense contexts, this includes continuous monitoring for security vulnerabilities and ensuring continued compliance with evolving standards.
A deployed satellite communications system would require regular security patches, compliance checks against updated NIST standards, and periodic recertification to maintain authorization to operate.
| Maintenance Phase Activities | Government/Defense Considerations |
| Continuous Monitoring | Real-time security monitoring for unauthorized access attempts |
| Patch Management | Secure distribution and implementation of updates |
| Performance Optimization | Regular reviews to maintain required performance levels |
| Change Management | Controlled process for implementing system modifications |
| System Retirement | Secure decommissioning including media sanitization and disposal |
III. Why SDLC is Critical for Government and Defense Projects
The system development life cycle is particularly crucial in government and defense sectors due to the high stakes involved. These projects support national security, military operations, and essential government services where failure is not an option.
Government and defense systems often process classified information, control critical infrastructure, or support military operations. The SDLC provides the structured approach necessary to ensure these systems meet stringent security, reliability, and performance requirements while complying with complex regulatory frameworks.
| Critical Factors | SDLC Mitigation Approach |
| National Security Implications | Formal security reviews at each phase, with explicit authorization gates |
| Regulatory Compliance | Documented traceability of requirements to implementation |
| Audit Requirements | Comprehensive documentation and version control throughout development |
| Long Operational Lifespans | Design for maintainability and secure updating over decades |
| System Interoperability | Structured testing of interfaces with legacy and current systems |
The SDLC’s phased approach ensures that government and defense projects adhere to standards like NIST SP 800-37 (Risk Management Framework), DoD 5000 series (Defense Acquisition), and agency-specific requirements.
By following established SDLC methodologies, project teams can demonstrate due diligence in addressing security concerns, managing risks, and meeting compliance requirements—essential considerations when developing systems that may be subject to congressional oversight or public scrutiny.
IV. Key Challenges in Implementing SDLC for Large-Scale Engineering Projects
While the SDLC provides a valuable framework, implementing it effectively in large-scale government and defense projects presents significant challenges.
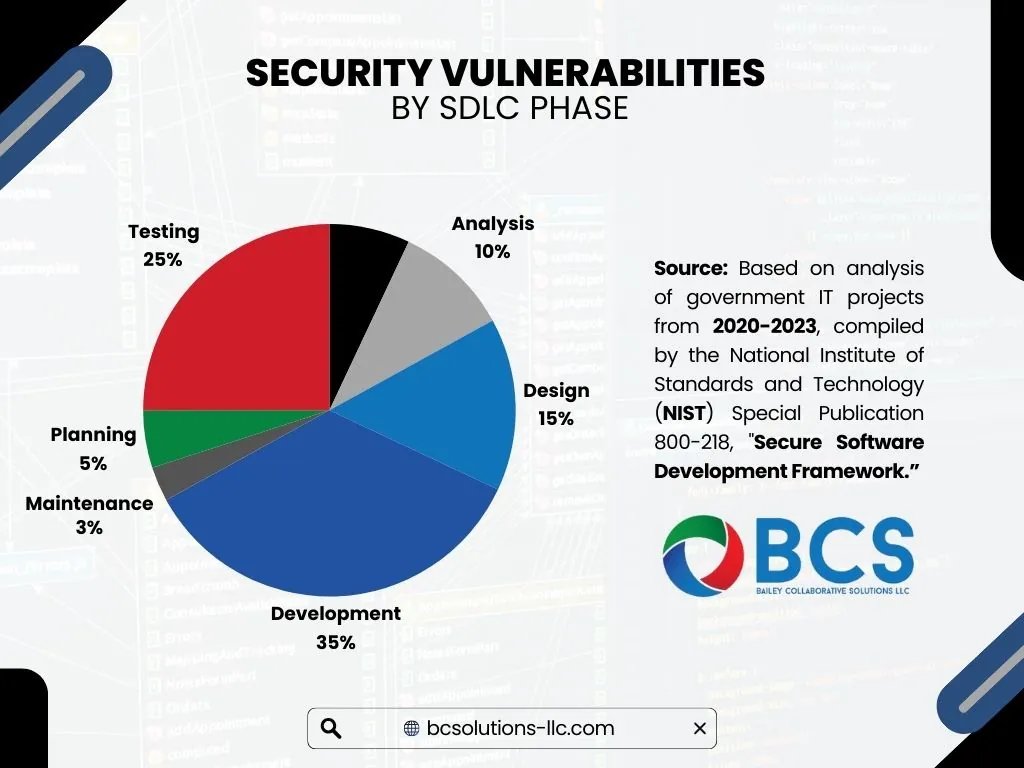
1. Security Integration Complexities
Government and defense systems must implement robust security controls while maintaining usability and performance. Integrating security at every phase of the SDLC is essential but challenging, particularly when working with classified requirements or advanced threat models.
| Challenge | Traditional Approach | Modern SDLC Approach |
| Threat Modeling | Performed late in development | Integrated from project inception |
| Security Testing | Conducted as final verification | Continuous throughout development |
| Classification Management | Separate tracks for classified/unclassified | Integrated classification management |
| Supply Chain Security | Limited vendor assessment | Comprehensive supply chain risk management |
2. Legacy System Integration
Many government and defense projects must integrate with legacy systems that may be decades old, operate on obsolete platforms, or lack modern security features. The SDLC must accommodate these integration challenges while ensuring the new system meets current standards.
| Challenge | Traditional Approach | Modern SDLC Approach |
| Interface Design | Point-to-point connections | Service-oriented architecture |
| Data Migration | One-time bulk transfer | Phased migration with verification |
| Security Gaps | Accepted as unavoidable | Mitigated through compensating controls |
| Documentation | Often incomplete for legacy systems | Reverse engineering and documentation |
3. Budget and Schedule Constraints
Government and defense projects often face strict budgetary constraints and inflexible schedules driven by appropriation cycles or operational needs. The SDLC must be tailored to deliver critical capabilities within these constraints while maintaining quality.
| Challenge | Traditional Approach | Modern SDLC Approach |
| Fixed Budgets | Feature reduction to meet budget | Value-based prioritization |
| Schedule Pressure | Compressed testing phases | Risk-based testing prioritization |
| Changing Requirements | Significant cost and schedule impact | Agile incorporation of changes |
| Personnel Turnover | Knowledge gaps during transitions | Comprehensive knowledge management |
4. Compliance and Certification Hurdles
Government and defense systems must comply with numerous regulations and often require formal certification before deployment. Navigating these requirements while maintaining development momentum presents a significant challenge.
| Challenge | Traditional Approach | Modern SDLC Approach |
| Authorization to Operate | The final hurdle before deployment | Progressive authorization approach |
| Documentation Burden | Extensive documentation at the project end | Continuous documentation throughout |
| Compliance Verification | Manual checklist reviews | Automated compliance verification |
| Multiple Oversight Bodies | Sequential approvals | Parallel processing with coordinated reviews |
V. Best Practices for a Successful SDLC in Government and Defense Engineering
Successfully implementing the SDLC in government and defense projects requires adaptation of industry best practices to meet the sector’s unique demands.
1. Aligning SDLC with Industry Standards
Adopting SDLC-recognized frameworks like CMMI, ISO 9001, or the NIST Risk Management Framework provides a solid foundation for SDLC implementation. These frameworks offer proven approaches that can be tailored to specific project needs while ensuring compliance with government requirements.
| Standard | Application in Government/Defense SDLC |
| CMMI | Process maturity assessment and improvement |
| ISO 9001 | Quality management system implementation |
| NIST RMF | Security risk management throughout lifecycle |
| DoD 5000 | Defense acquisition process alignment |
| IEEE 12207 | Software lifecycle processes |
2. Leveraging Advanced Engineering Tools
Modern tools can significantly enhance SDLC efficiency and effectiveness in government and defense projects. Model-Based Systems Engineering tools like Cameo, simulation platforms like MATLAB, and engineering tools like MapleSim enable more rigorous design, analysis, and verification activities.
| Tool Category | Government/Defense Applications |
| Requirements Management | Tracking classified and unclassified requirements with traceability |
| Model-Based Systems Engineering Tools | Creating verifiable system models with security attributes |
| Simulation Software | Testing system behavior under various operational conditions |
| Static Analysis Tools | Identifying security vulnerabilities in code |
| Configuration Management | Maintaining secure version control with audit trails |
3. Incorporating Automation
Automation reduces manual errors, improves consistency, and accelerates development activities. In government and defense projects, automation can be particularly valuable for security testing, compliance verification, and documentation generation.
| Automation Area | Benefits for Government/Defense SDLC |
| Build Processes | Consistent application of security controls |
| Security Testing | Regular vulnerability scanning and penetration testing |
| Compliance Checking | Automated verification against security baselines |
| Documentation | Generation of required documentation from system models |
| Deployment | Repeatable, secure deployment procedures |
4. Ensuring Stakeholder Collaboration
Effective collaboration between engineers, security specialists, program managers, and end users is essential for SDLC’s success. In government and defense projects, this often requires navigating organizational hierarchies, classification barriers, and complex approval chains.
| Collaboration Area | Government/Defense Considerations |
| Requirements Elicitation | Workshops involving operational personnel and security experts |
| Design Reviews | Multi-disciplinary teams including security specialists |
| Test Planning | Coordination with certification authorities and operational testers |
| Implementation Planning | Involvement of cybersecurity and system administration teams |
| Change Management | Formal configuration control boards with security representation |
VI. How BCS Helps Organizations Optimize Their SDLC Process
Bailey Collaborative Solutions (BCS) specializes in guiding government and defense organizations through complex system development challenges. With deep expertise in both technical engineering and regulatory requirements, BCS provides tailored SDLC solutions that meet the sector’s unique demands.
1. Expert Guidance in Systems Engineering
BCS offers specialized knowledge in systems engineering for defense, space, and government sectors. By combining industry best practices with sector-specific expertise, BCS helps organizations implement effective SDLC processes that balance security, compliance, and innovation.
| BCS Service Area | SDLC Enhancement |
| Requirements Engineering | Clear, testable requirements that align with mission needs |
| Systems Architecture | Security-focused architectures that meet defense standards |
| Digital Engineering & The Future | Advanced modeling and simulation for complex systems |
| Digital Quality Engineering | Rigorous verification and validation approaches |
| Test Engineering | Comprehensive test strategies for mission-critical systems |
2. Training the Next Generation
BCS not only provides immediate expertise but also focuses on developing engineering talent through mentorship and knowledge transfer. This approach ensures organizations build internal capabilities for long-term SDLC success.
| Training Approach | Organizational Benefit |
| Mentorship Programs | Knowledge transfer from experienced engineers to junior staff |
| Process Documentation | Capture of institutional knowledge and best practices |
| Tool-Specific Training | Skill development in key SDLC tools and technologies |
| Security Education | Building security awareness throughout development teams |
| Compliance Training | Understanding of regulatory requirements and processes |
3. Real-World SDLC Success
BCS has helped numerous organizations improve their SDLC processes, resulting in more efficient development, higher quality systems, and better compliance outcomes.
Consider a recent defense communications system project where BCS implemented a modernized SDLC approach. By introducing Digital Product Engineering techniques, automating security testing, and establishing a structured requirements management process, BCS helped the client reduce development time by 30% while improving security compliance.
| SDLC Challenge | BCS Solution | Result |
| Inefficient Requirements Process | Structured elicitation and management approach | 40% reduction in requirements churn |
| Delayed Security Testing | Integrated security throughout development | Early vulnerability detection and resolution |
| Documentation Burden | Automated generation from system models | 60% reduction in documentation effort |
| Integration Complexities | Digital Platform Engineering approach | Simplified interfaces and reduced integration issues |
| Test Coverage Gaps | Comprehensive test automation | Improved defect detection and system reliability |

Conclusion: Why a Strong SDLC Strategy is the Key to Success in Government and Defense Engineering
The system development life cycle provides an essential framework for navigating the complexities of government and defense system development. By breaking the process into manageable phases with clear objectives and deliverables, the system development life cycle enables organizations to develop secure, reliable systems that meet mission requirements while complying with regulatory standards.
As technology evolves and threats become more sophisticated, implementing an effective SDLC becomes increasingly critical. Organizations must not only follow the basic SDLC framework but also adapt it to address emerging challenges in cybersecurity, integration, and compliance.
Bailey Collaborative Solutions stands ready to help government and defense organizations optimize their SDLC processes. With deep expertise in systems engineering, Digital Engineering Tools, and regulatory compliance, BCS provides the guidance needed to navigate complex development challenges successfully.
For organizations seeking to enhance their system development capabilities, improve project outcomes, or address specific SDLC challenges, consulting with BCS offers a path to more efficient, secure, and compliant system development. By partnering with experienced systems engineering experts, government and defense organizations can ensure their critical systems meet the highest standards of quality, security, and performance throughout the entire development lifecycle.